The Workstation Blog
Security
Posts tagged Security.
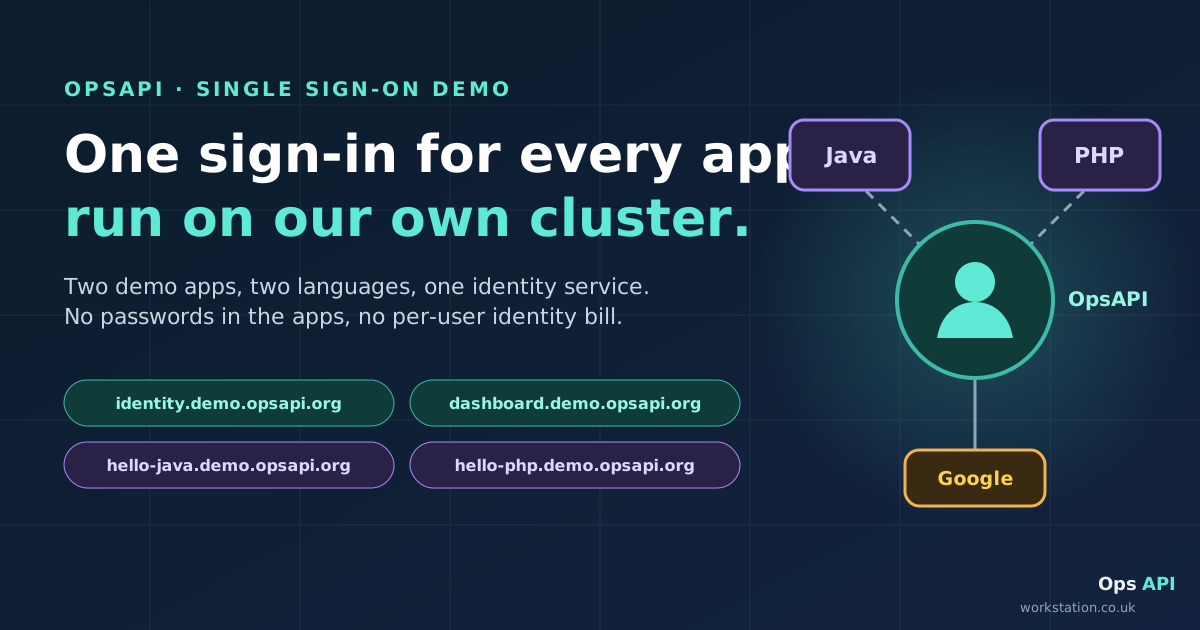
One Sign-In for Every App, Run on Our Own Cluster
Five demo apps in five languages never see a password and never talk to Google: they send users to a self-hosted OpsAPI, which signs them in and hands back a token the app checks with one API call. What it costs to add an app, why admin dashboards belong behind a VPN or zero-trust broker, and the honest limits.
 Balinder WaliaRead
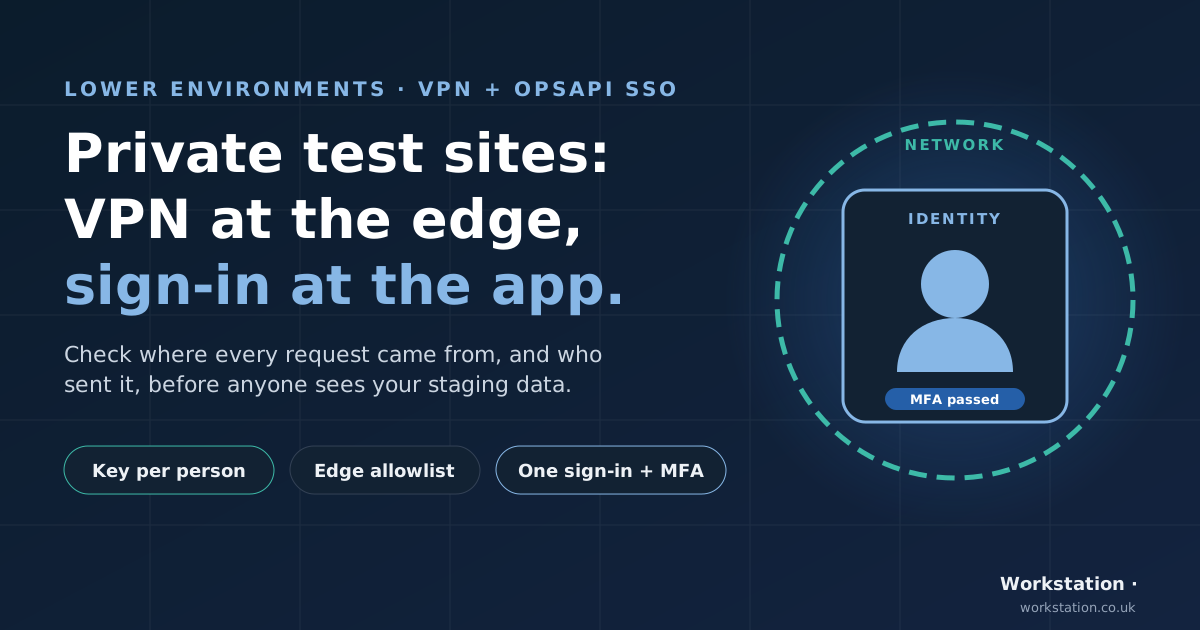
Keep Your Test Sites Private: VPN at the Edge, One Sign-In for Every App
Staging and test sites hold real-looking data, yet they're often protected by an IP allowlist alone. Here's how two layers keep them private: a VPN checked at the edge proves where a request came from, and one OpsAPI sign-in with MFA proves who sent it, across every app.
Balinder WaliaRead 
Put Internal Apps Behind Your VPN, Without Rebuilding Them
Staging sites and admin panels are often 'private' because of an IP allowlist. Put them behind the wslvpn Zero Trust VPN, enforced at the WSLProxy edge: check the tunnel and the person, fail closed, and see why someone was blocked. One field per domain, no app changes, no reload.
Balinder WaliaRead 
Gemini 4 Argon: What It Means for Your Team, and Where to Use It First
Gemini 4 Argon is built to work for hours on one measurable problem. Here is what shipped, the real costs, and how to pilot it safely on your own backlog.
Balinder WaliaRead 
WSL Vault for Compliance: One Tenant Never Opens Another’s Secrets
How WSL Vault keeps app, team, and environment tenants cryptographically isolated — so a stolen root-style token cannot empty the estate — and why dual-tenant control beats secrets sprawl.
Balinder WaliaRead 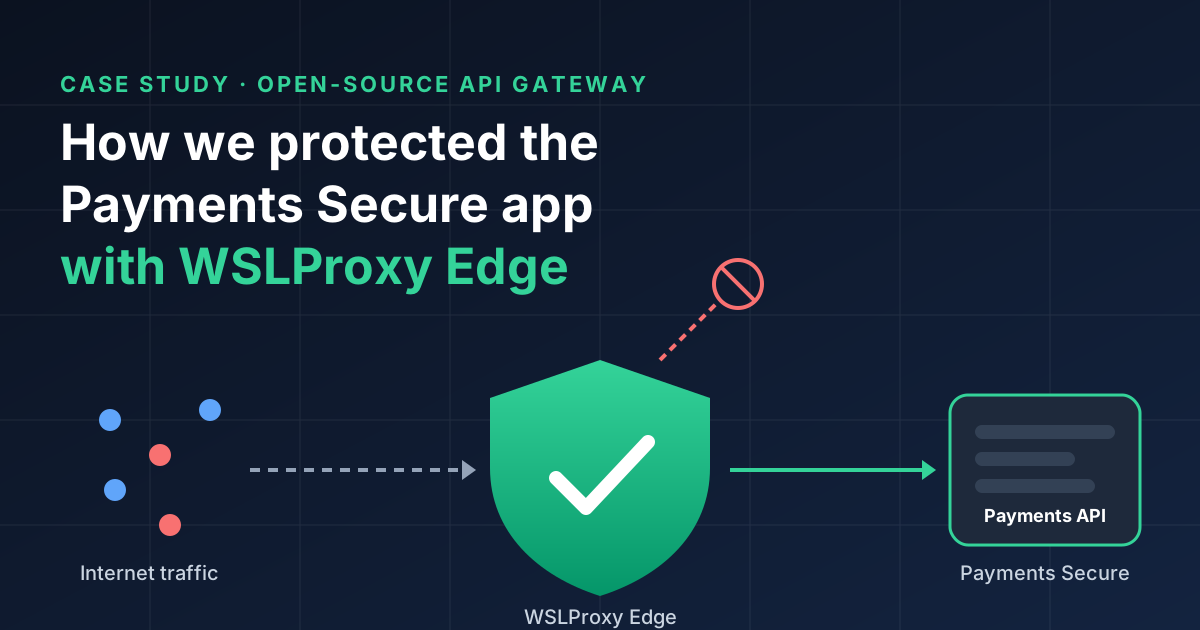
How We Protected the Payments Secure FinTech App with WSLProxy Edge, an Open-Source API Gateway
How we put WSLProxy Edge, our open-source API gateway, in front of Payments Secure (payments-secure.fictionally.org): real-IP checks, scanner detection, login throttling and audit logs, rolled out safely in audit mode.
Balinder WaliaRead 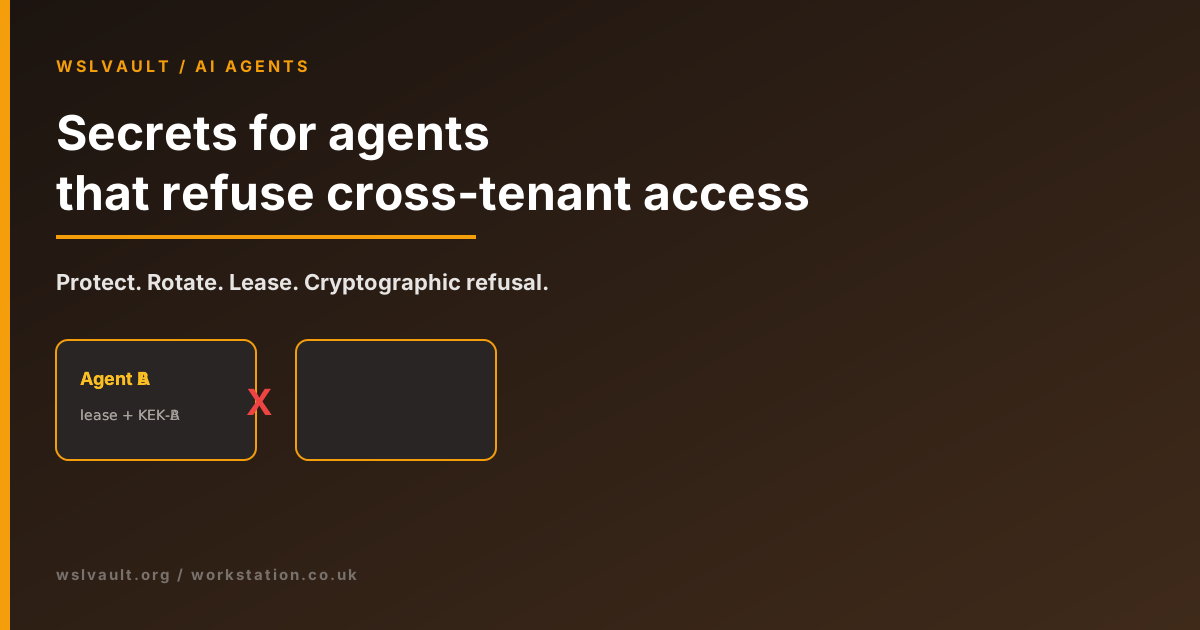
WSLVault: Why AI Agents Need Cryptographic Secrets Isolation
AI agents use secrets at machine speed across tools and tenants. WSLVault seals per tenant so a shared platform never leaks another team's plaintext.
Balinder WaliaRead 
Jobshout SEO Analyst AI Agent — Analyse Any Website & Fix SEO Issues Automatically
We ran Jobshout SEO Analyst on workstation.co.uk — score 44/100 — with concrete fix prompts for missing H1, truncated title, and oversized meta description.
Balinder WaliaRead 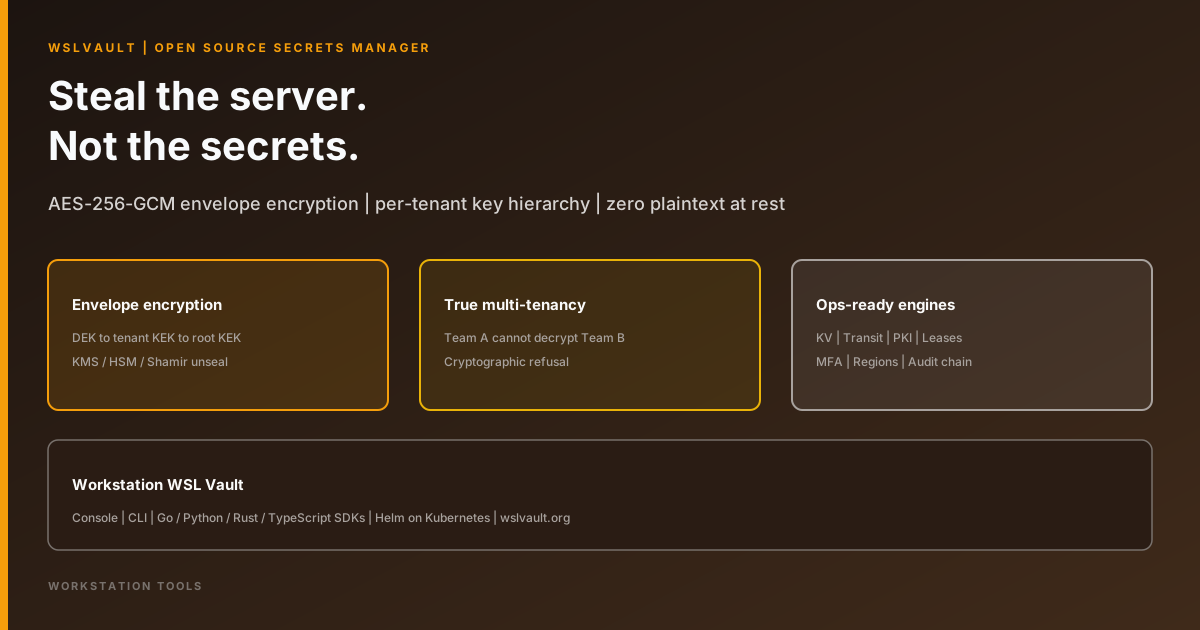
WSLVault: Steal the Server. Not the Secrets.
WSLVault seals secrets before they touch disk — DEK to tenant KEK to root KEK — so a stolen host still leaves attackers with ciphertext they cannot open.
Balinder WaliaRead 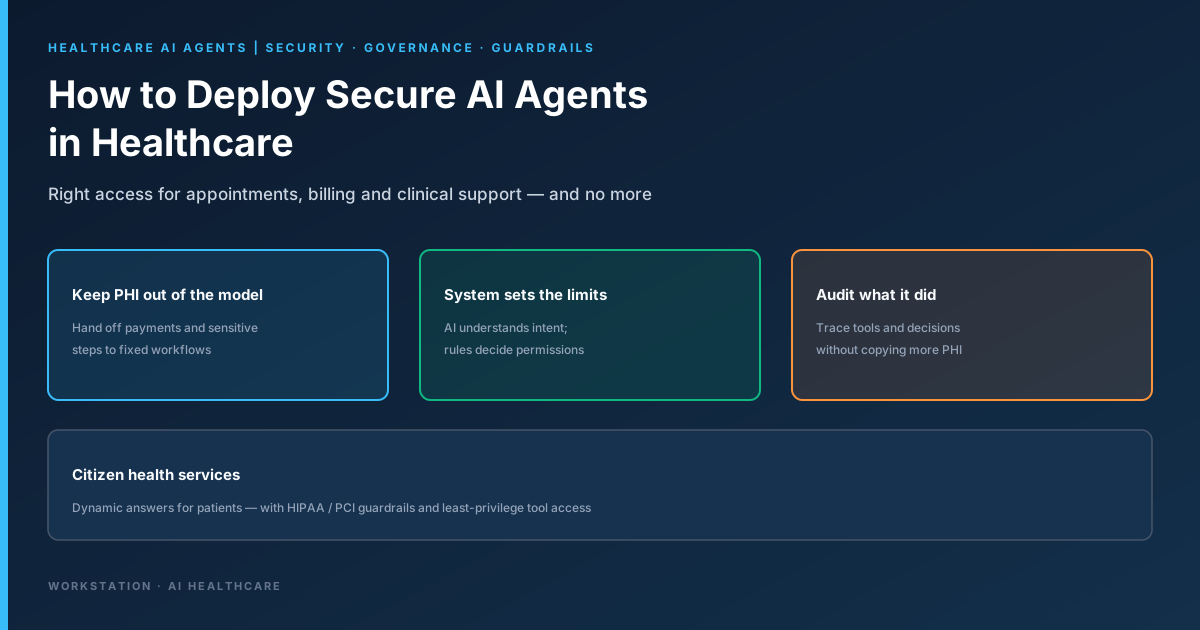
How to Deploy Secure AI Agents in Healthcare
AI agents can book appointments, take payments and support clinical work. Here is how healthcare teams can give them the right access, and no more.
Balinder WaliaRead 
WSLProxy WAF Engine v2: Enterprise Enforcement You Can Explain
Workstation WSL Proxy WAF Engine v2: governed stages and signatures on the OpenResty hot path — explainable enforcement with support IDs.
Balinder WaliaRead WSL Proxy WAF: Explainable Web Application Firewall at the Edge
Workstation WSL Proxy WAF: governed stages and signatures on a live-config OpenResty edge — monitor or block, with explainable support IDs.
Balinder WaliaRead 
Workstation WSL Proxy: API Gateway, CDN & Agent Edge
Workstation WSL Proxy (WSLProxy) is a complete API gateway and CDN edge: live routing, WAF, cache, multi-POP DNS, MCP — with Agents Gateway and MCP Gateway in progress.
Balinder WaliaRead 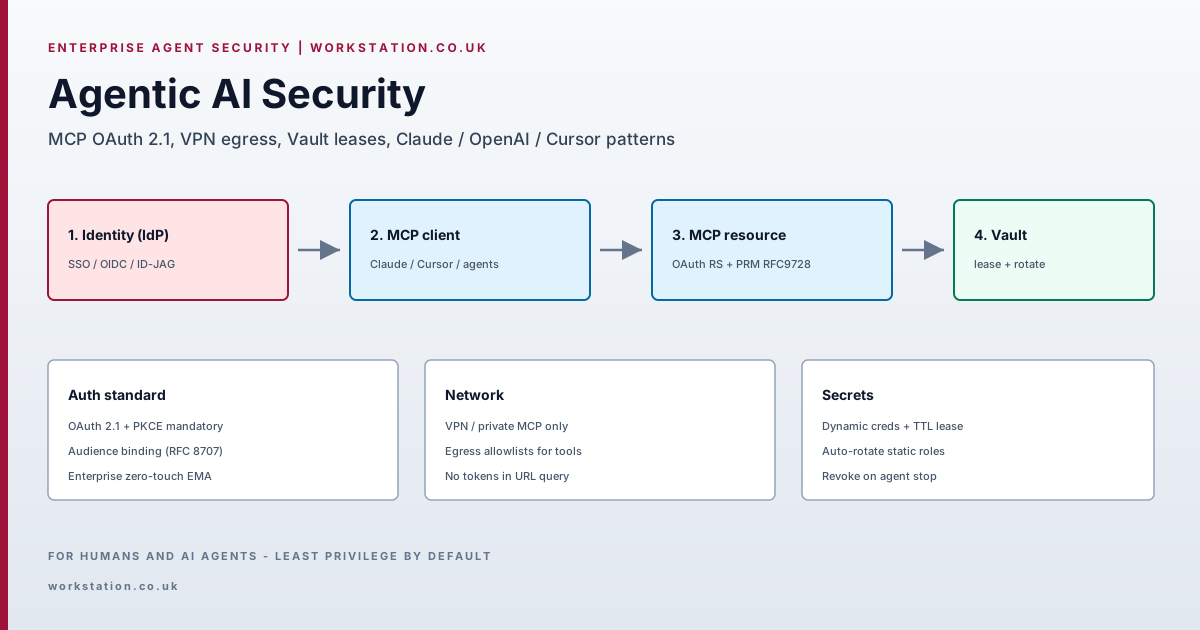
Agentic AI Security: MCP OAuth, VPN & HashiCorp Vault Leases
Secure enterprise AI agents with MCP OAuth 2.1, VPN-isolated tools, and HashiCorp Vault leases that auto-rotate and expire — plus Claude, OpenAI, and Cursor recommendations.
Balinder WaliaRead 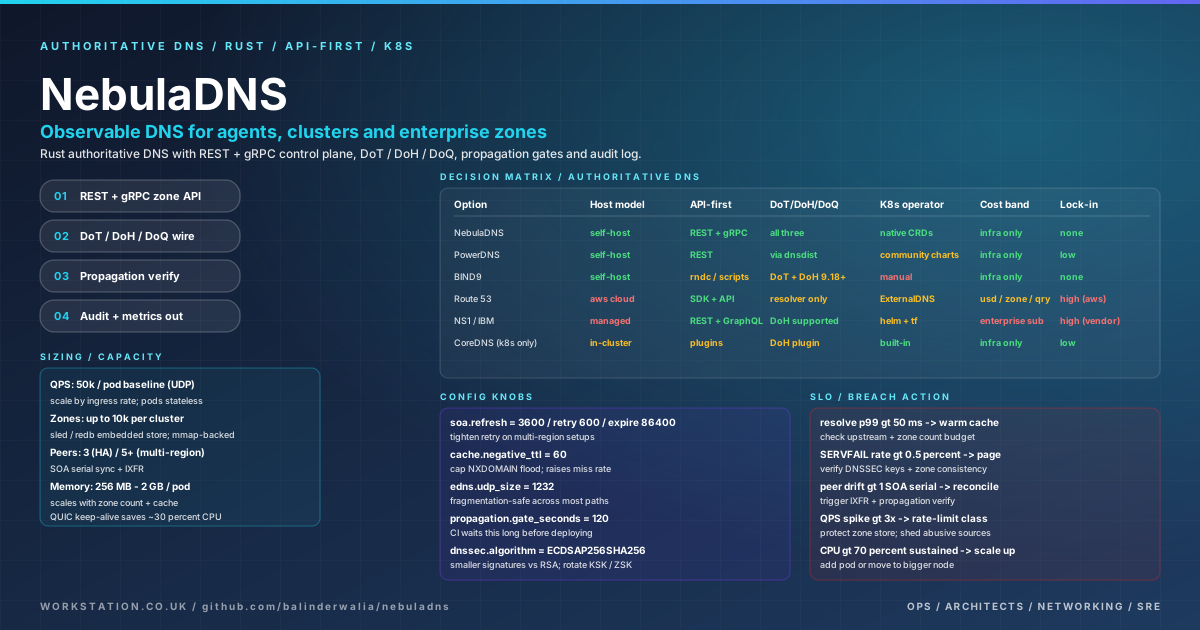
NebulaDNS Complete Feature Guide: k3s, Route53, Observability, and Enterprise DNS
Complete tour of NebulaDNS features: API-first control plane, Prometheus metrics, propagation gates, peer fingerprinting, DNSSEC roadmap, Helm/k3s operator story, and how to integrate with AWS Route 53 and CoreDNS.
Balinder WaliaRead NebulaDNS: Why Authoritative DNS Is a Game Changer in the AI Era
NebulaDNS is a safe-Rust authoritative DNS server with an API-first control plane, Prometheus metrics, propagation gates, and Kubernetes-native operations—built for visibility when AI services and agents depend on DNS more than ever.
Balinder WaliaRead 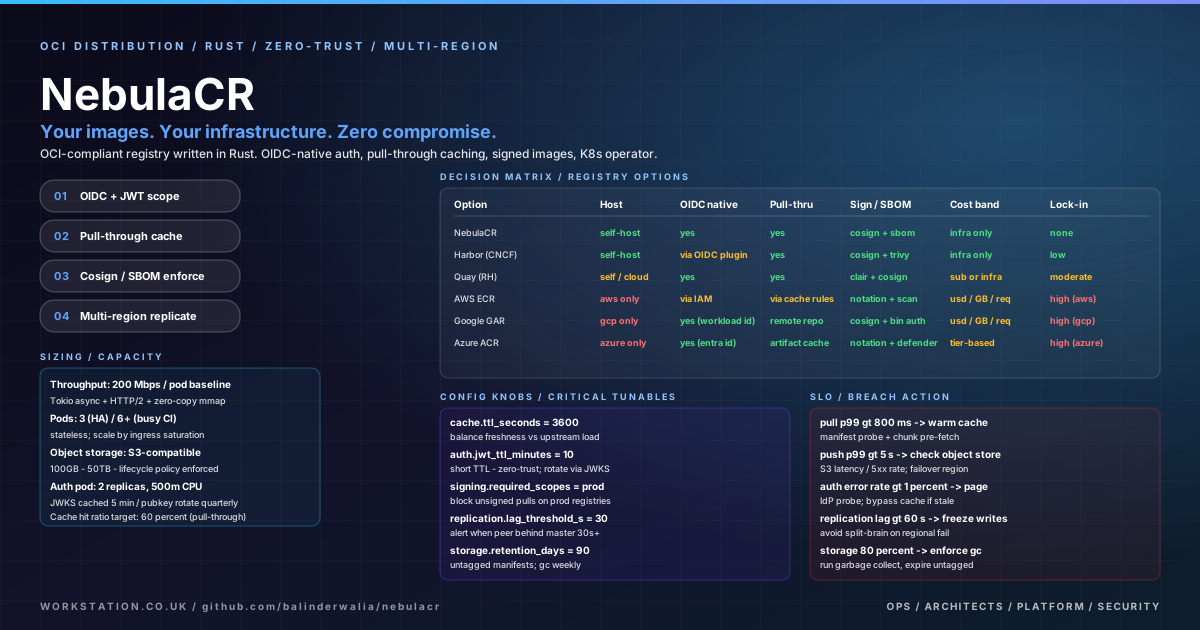
NebulaCR: Enterprise OCI Registry, Observability, and Compliance Without Compromise
Professional overview of NebulaCR: Rust OCI registry with nebula-registry and nebula-auth, zero-trust OIDC for humans and CI, SCIM lifecycle, Prometheus and OpenTelemetry, multi-region replication, pull-through cache, and Kubernetes Helm deployment—synthesised from the upstream docs/ and README.
Balinder WaliaRead