Workstation Logo
उत्पाद
एआई लैब्सOpenAI एजेंट्सClaude एजेंट्सGrok BotWorkstation CRM (WSL CRM)मार्केटिंगसभी उत्पाद
एआई समाधान
एआई वर्कस्टेशनAI SME Packagesप्राइवेट एआईजीपीयू क्लस्टरएज एआईएंटरप्राइज एआई लैबउद्योग अनुसार एआई
सेवाएँ
Platform ModernisationDigital EngineeringData Foundations & AIAutonomous Operationsएआई परामर्शDevOps स्वचालनसाइबर सुरक्षासॉफ़्टवेयर विकासएजेंट निर्माणMLOps सेटअप
हमारे बारे में
साझेदारग्राहक कहानियाँ
लेख
प्रलेखन
WSL ProxyRing PromoterWSL VaultJobshoutSysOps 24/7
ब्लॉग
संपर्क करेंLogin
Workstation

आधुनिक व्यवसायों के लिए AI वर्कस्टेशन, AI मल्टी-एजेंटिक सॉफ़्टवेयर, GPU अवसंरचना और बुद्धिमान एजेंट समाधान।

संपर्क करें

AI समाधान

एआई वर्कस्टेशनAI SME Packagesप्राइवेट एआईजीपीयू क्लस्टरएज एआईएंटरप्राइज एआई लैबउद्योग अनुसार एआई

उत्पाद

सभी उत्पादWSL CRM और ERPमार्केटिंगOpenAI एजेंट्सWSL ProxyRing PromoterWSL VaultJobshoutSysOps 24/7

कंपनी

हमारे बारे मेंWorkstation क्योंसाझेदारग्राहक कहानियाँमूल्य निर्धारणसंपर्क

संसाधन

लेखप्रलेखनब्लॉगखोजेंसाइटमैप
यूके कार्यालय
77-79 Marlowes, Hemel Hempstead HP1 1LFदिशा-निर्देश - M25 आउटर लंदन से जंक्शन 20 लेंकंपनी संख्या: 11641870सोम - शुक्र: सुबह 9:00 - शाम 6:00 GMT
+44 7515 356 146
बेल्जियम कार्यालय
Workstation SRL, Rue Vanderkindere 34, 1180 Uccle, BrusselsBE 0751.518.683सोम - शुक्र: सुबह 9:00 - शाम 6:00 CET
+32 492 45 67 46
भारत कार्यालय
#159 Sector 9, Pocket 1, DDA Flats, 110077 Dwarka, New Delhi
+91 98881 98841

© 2026 Workstation AI. सर्वाधिकार सुरक्षित।

गोपनीयताकुकीज़सेवा की शर्तेंवेबसाइट साइटमैप

Loading blog...

Home / Blog
DevOpsSecuritySREKubernetesAI

WSLVault: Steal the Server. Not the Secrets.

Open-source secrets manager with envelope encryption, true multi-tenancy, KV/transit/PKI/leases, multi-region HA, and hash-chained audit
Balinder Walia22 सितंबर 20261 min read

Steal the server. Not the secrets. WSLVault is an open-source, self-hosted secrets manager built on AES-256-GCM envelope encryption and a per-tenant key hierarchy. This intro covers what it is, why the model matters, and how you drive it from console, CLI, or SDKs. Deep dive: long article · Product: /wsl-vault.
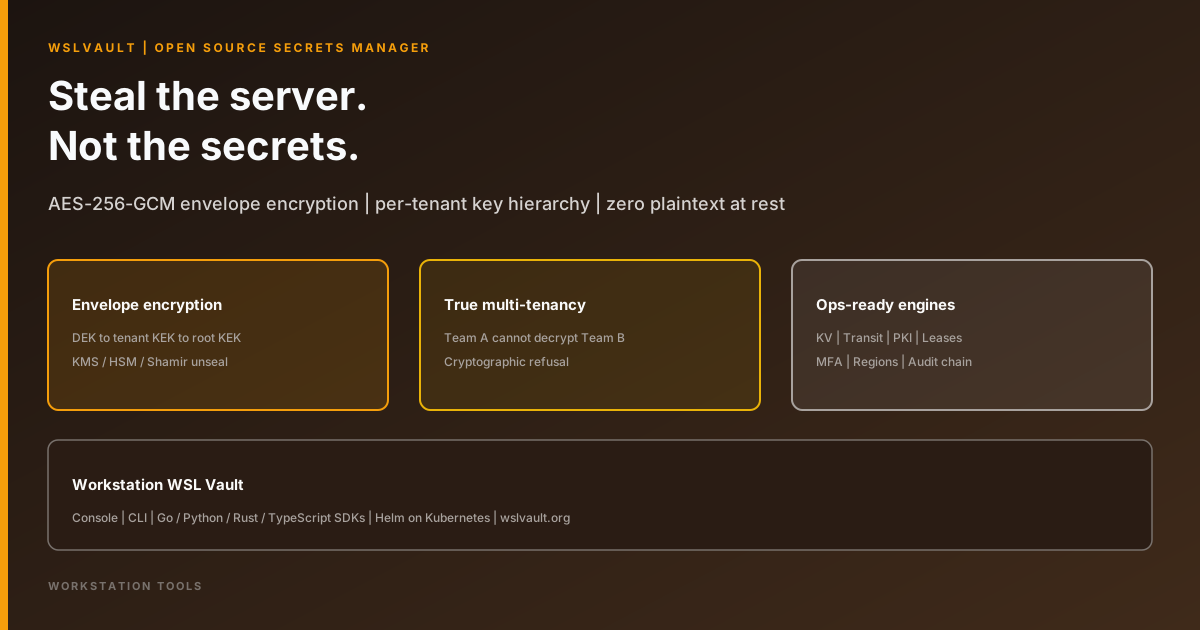
WSLVault — steal the server, not the secrets

Watch on YouTube (~20 min)

Bottom line. A stolen disk, database dump, or compromised host should leave attackers with ciphertext they cannot open. WSLVault seals every secret before storage — DEK → tenant KEK → root KEK — so multi-tenancy is cryptographic, not cosmetic.

WSLVault is built for operators who want Vault-compatible workflows without plaintext at rest: Rust services, Helm/GitOps on Kubernetes, CLI plus Go/Python/Rust/TypeScript SDKs, and a steel/brass web console.

What you will learn

  • True multi-tenancy — Team A cannot decrypt Team B (cryptographic refusal, not “oops”)
  • Envelope encryption — DEK → tenant KEK → root KEK (KMS / HSM / Shamir)
  • Engines — KV secrets, transit encryption, PKI, dynamic leases, MFA
  • Operations — Active/active multi-region replication and tamper-evident, hash-chained audit
  • Why it matters — Steal the disk ≠ steal the secrets
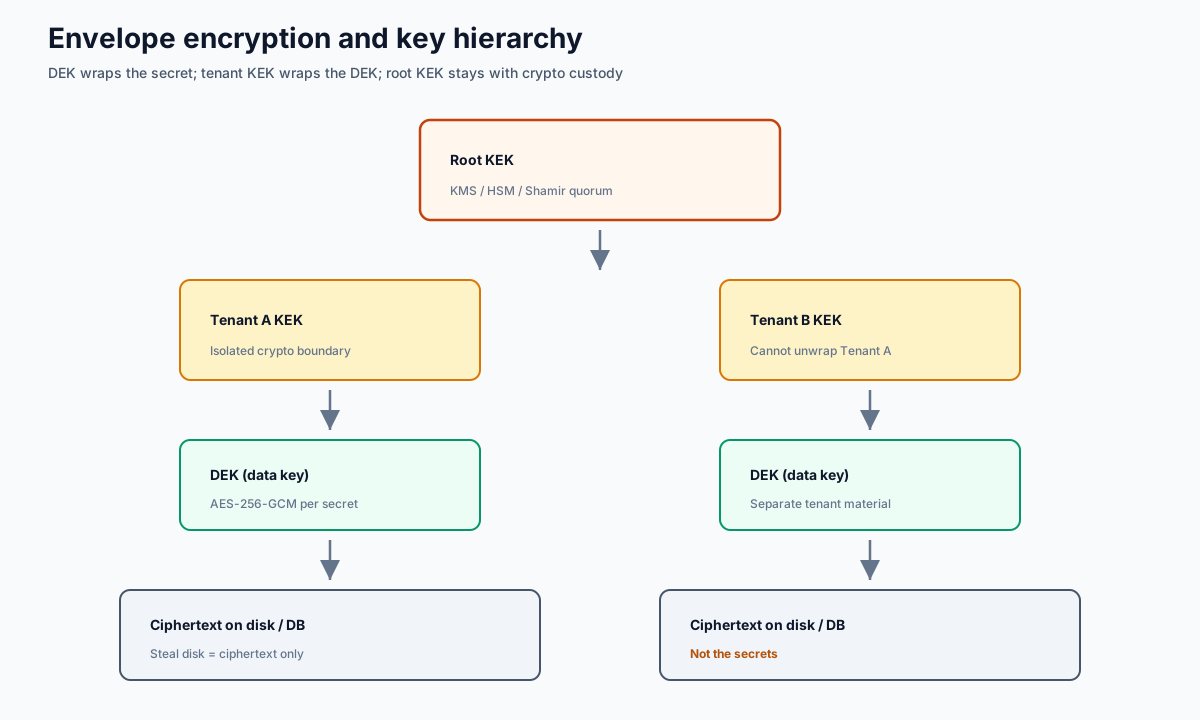
WSLVault envelope encryption key hierarchy

Links

  • Site: https://www.wslvault.org/
  • GitHub: https://github.com/bwalia/wslvault
  • Docs: docs/
  • Getting started: GETTING-STARTED.md
  • Workstation product page: /en/wsl-vault

Read the full technical brief · Open the WSL Vault tools page